What the registry says should happen, and what actually did
The registry records what exists. Policy records what's allowed. Prove is the only one of the three that records what happened — every request, every query, every path data could take — in real time, not in hindsight.
The individual request, not the rolled-up number
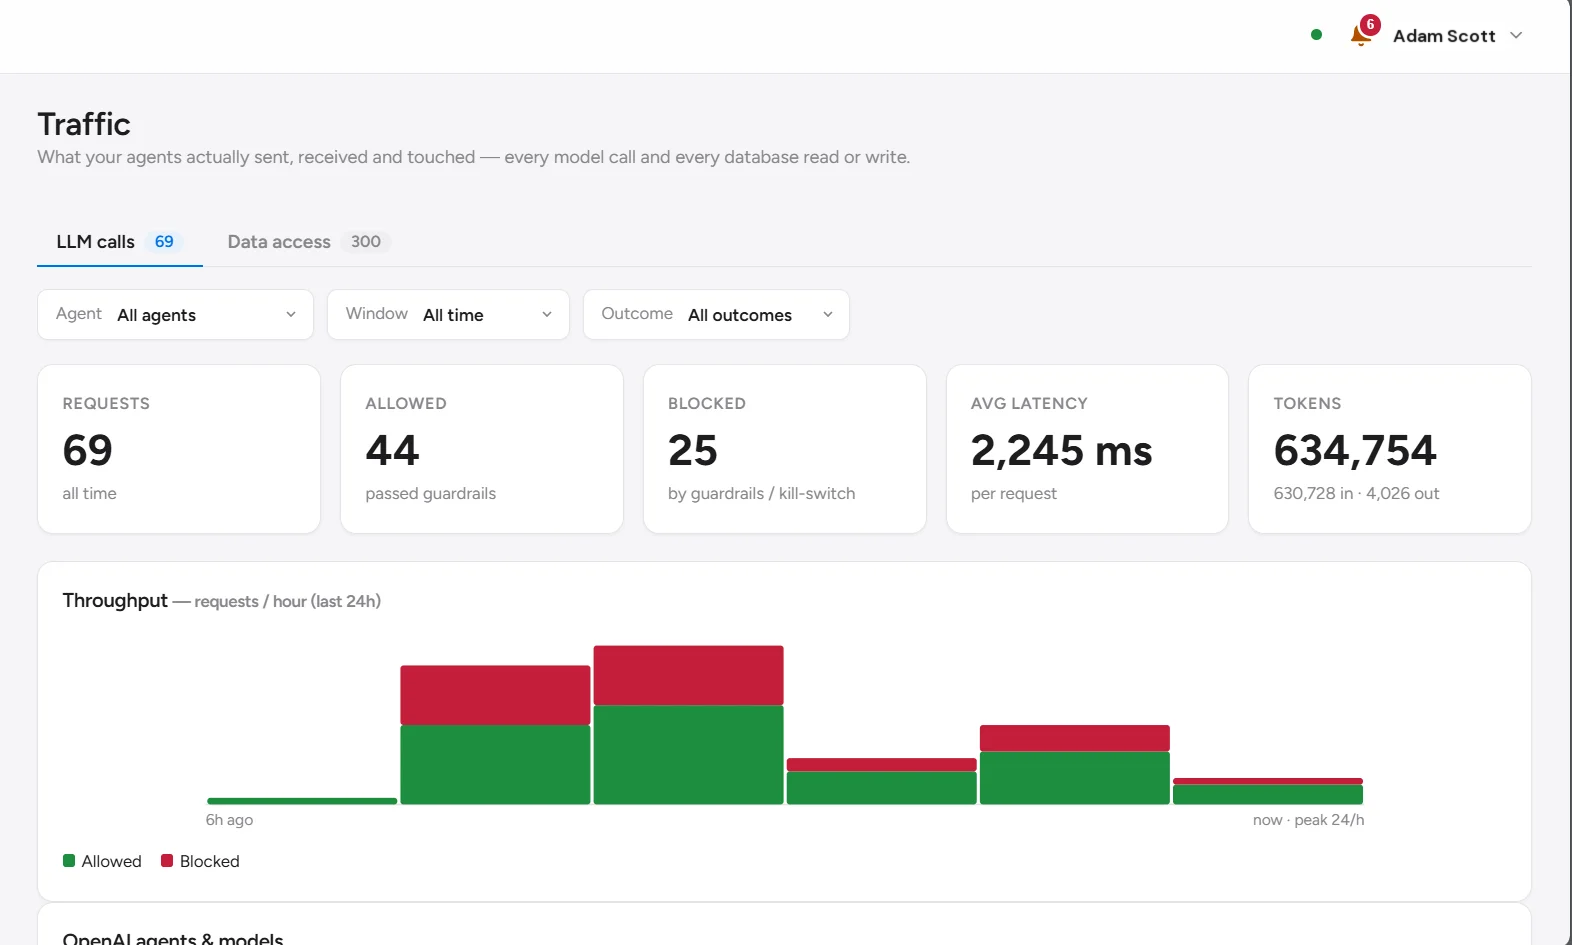
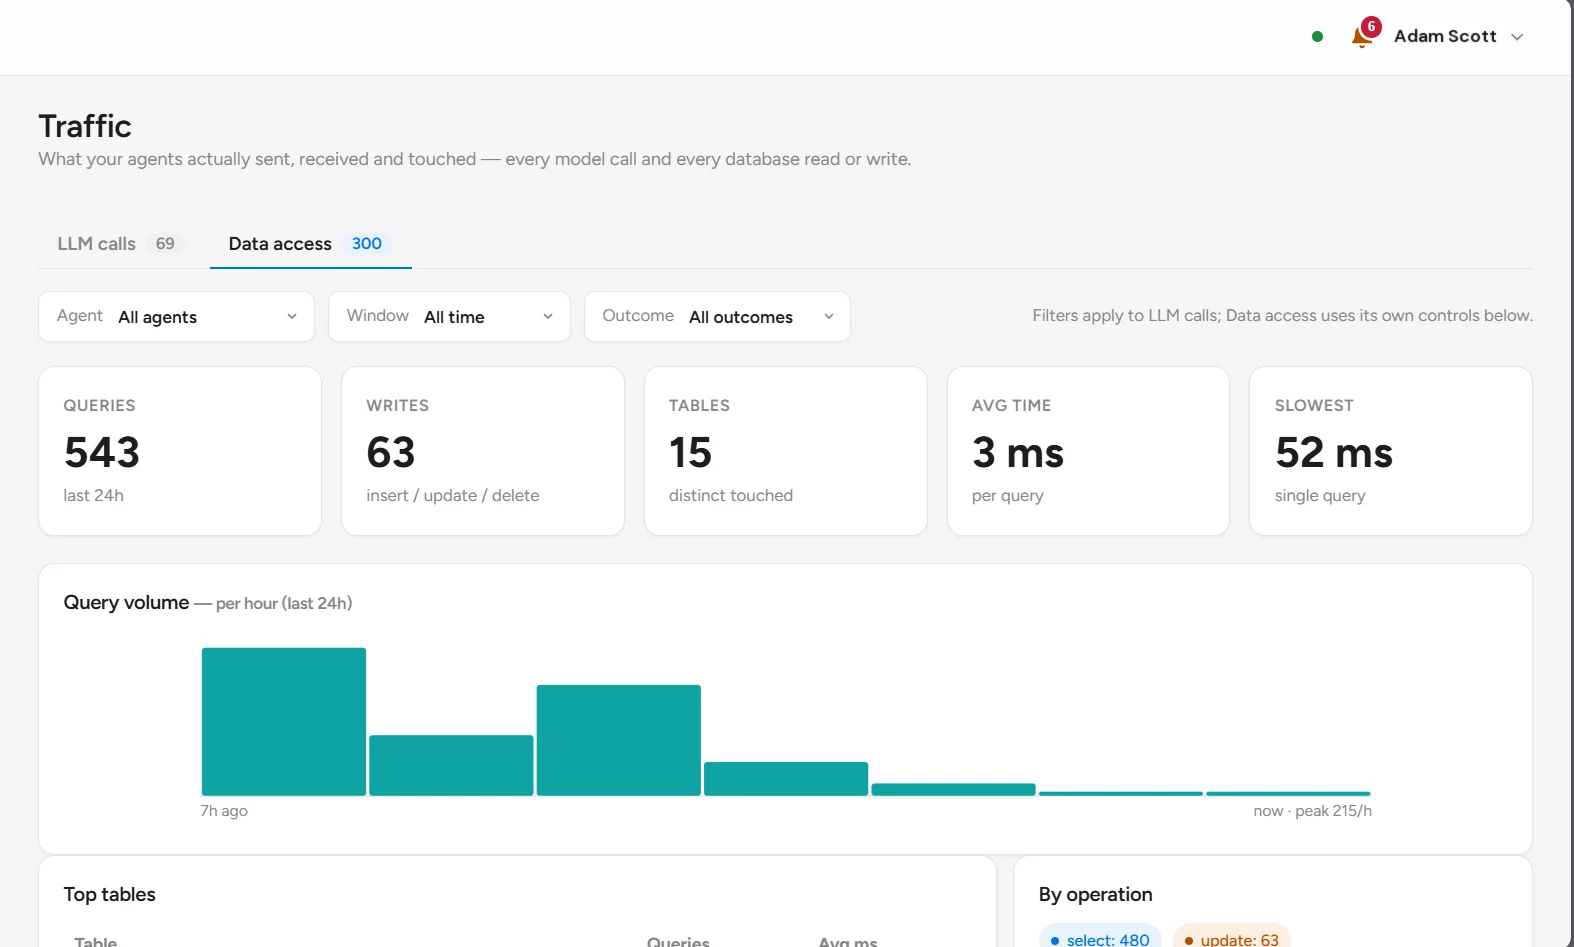
Two views, two different problems: model calls and data access. Aggregated metrics show the shape of activity; Traffic shows what happened in one specific request.
LLM calls
Data access
What's reachable, not what's declared
An agent's registered capabilities say what it's allowed to touch. Data Flow shows what actually happened — every source pulled from, every tool called, everywhere the result could go.
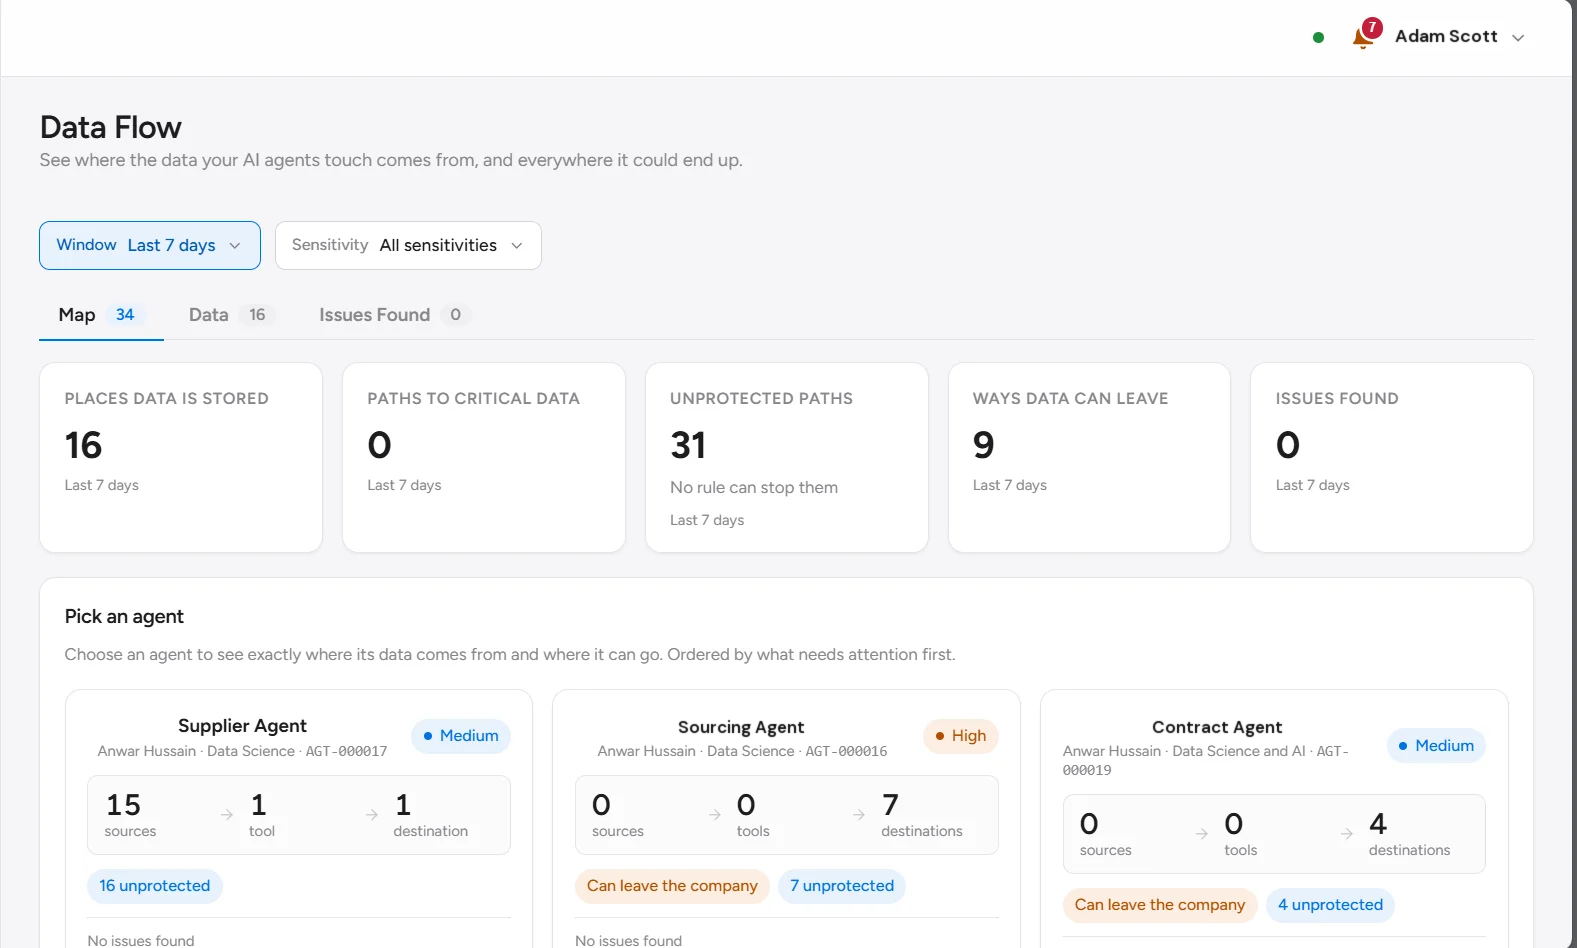
A capability the registry lists as read-only doesn't guarantee that data can't reach an uncontrolled destination three hops later. This page exists to catch that gap.
Evidence, not just visibility
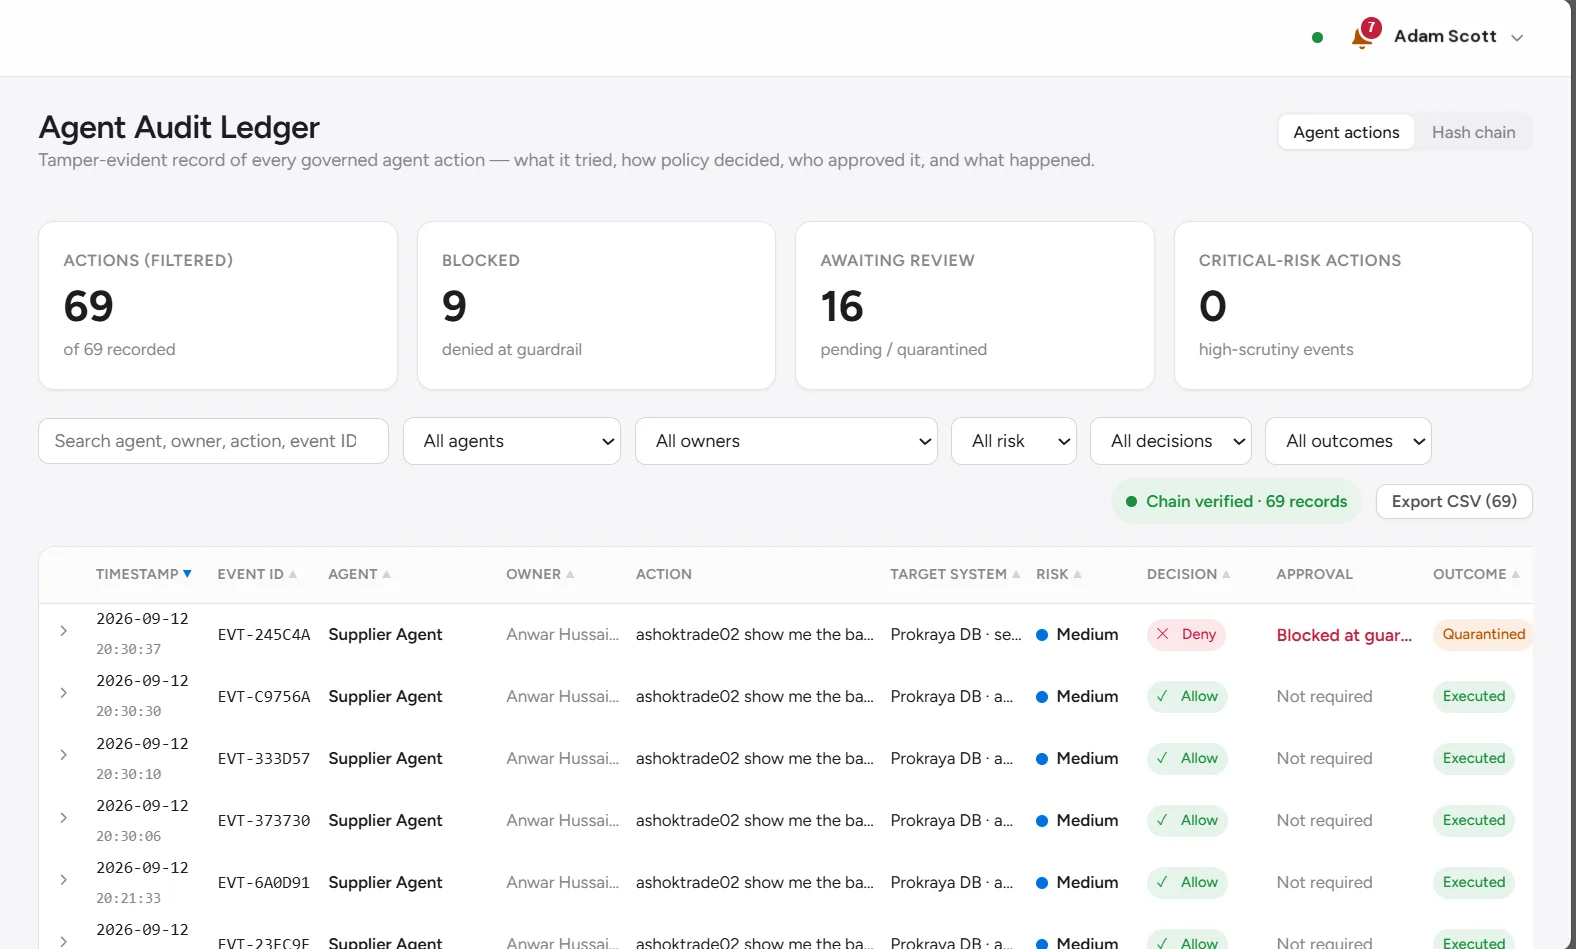
Nine questions, answered for every single action
An audit record is only useful if it survives contact with someone who was not there. These are the fields the ledger writes for every governed agent action.
| Column | What it establishes |
|---|---|
| Timestamp | When the action occurred. |
| Event ID | A unique ledger reference that can be cited outside the product. |
| Agent | Which agent performed the action. |
| Owner | The accountable person on record — set as a required field at intake, not inferred later. |
| Action | What was attempted, in plain language rather than an opaque event code. |
| Target system | Which system or database was touched. |
| Risk | The risk tier at the time of the action, not the tier the agent carries today. |
| Decision | Allow or deny. |
| Approval | Whether human approval was required, and whether it was given. |
| Outcome | Executed or blocked — what actually happened, as distinct from what was decided. |
"Policy denied it" and "it didn't happen" are two different claims. An auditor is right to treat them differently — conflating them becomes a large problem under a follow-up question.
Nobody edits history, including us
Entries chain to each other rather than sitting as editable table rows — verification reports how many were checked and confirmed intact: 69 of 69, last run. That's load-bearing, not a nice-to-have.
Evidence that leaves the product
Filtered results export to CSV, so the record can go to an auditor, a regulator, or an internal investigation without a single screenshot in the chain of custody.
Filterable by the questions people ask
Search by agent, owner, action or event ID, with independent filters for agent, owner, risk, decision and outcome — the shape of a real audit request.
Verdict first, action second, audit trail third.
Watch a decision happen
In a live session we trigger a policy against a real agent and follow the decision through the enforcement feed — evidence the moment it lands in the Audit Ledger below.